EngineeringUpdated
Passkeys: Should Your App Drop Passwords?
Passkeys let people sign in with a fingerprint, face or device PIN instead of a password. What they are, why they stop phishing and how to add them to your app.
By Visionite Tech Team
What a passkey is
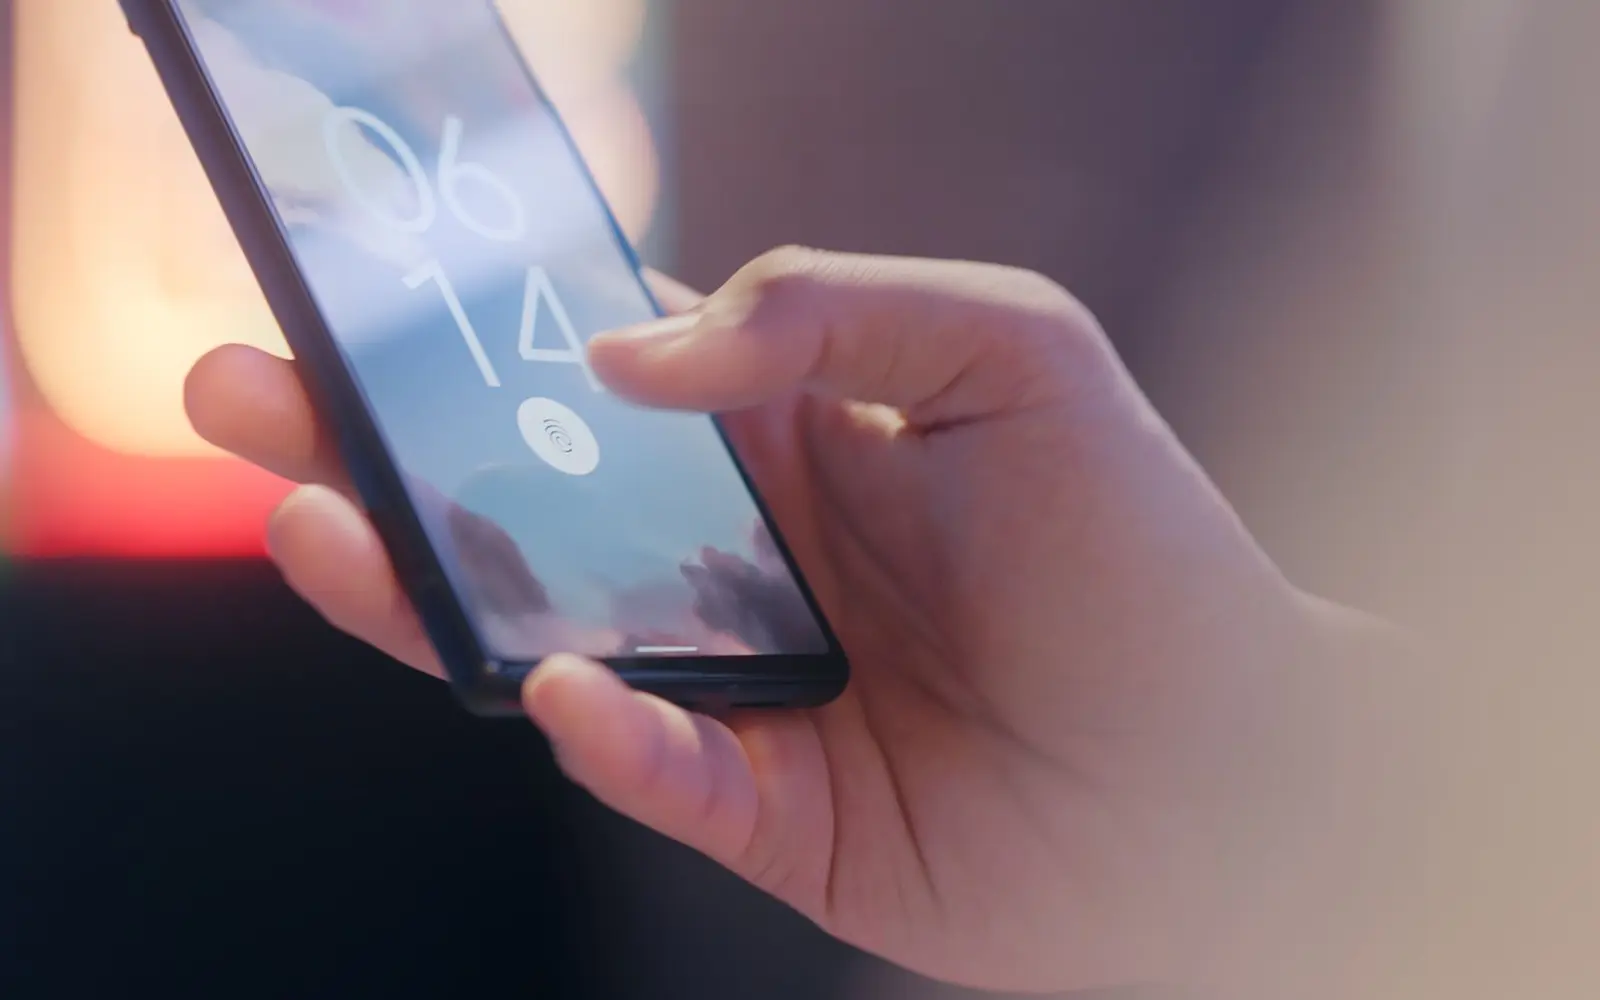
A passkey is a sign-in credential based on the FIDO and WebAuthn standards. It is a pair of keys: the private key stays on the user's device or in their password manager, and your server stores only the public key. To sign in, the user unlocks the passkey with a fingerprint, face scan or device PIN.
Passkeys sync across devices through Apple iCloud Keychain, Google Password Manager and password managers such as 1Password, so a lost phone doesn't mean a lost account.
Why they matter
- Phishing-resistant: a passkey only works on the website or app it was created for, so a fake login page can't use it.
- Nothing useful to steal: a leaked database of public keys can't be used to sign in.
- Faster sign-in: a fingerprint or face scan replaces typing a password, and resetting one.
- Fewer support tickets for forgotten passwords and locked accounts.
Adoption is no longer a question. On World Passkey Day 2026, the FIDO Alliance estimated that about 5 billion passkeys are now in use worldwide, and Google, Apple, Microsoft, Amazon and PayPal all offer them.
Where they work today
Passkeys are supported on iOS, Android, Windows and macOS, and in Chrome, Safari, Edge and Firefox. Most of your users already have a device that can create one.
How to add passkeys to your app
- Offer them alongside your current sign-in first, not instead of it.
- Invite users to create one right after a successful sign-in, when they trust the moment.
- Use a maintained library or auth provider, such as SimpleWebAuthn, Auth0 or Clerk, rather than writing the cryptography yourself.
- Turn on passkey autofill, so the browser suggests the passkey in the username field.
- Plan account recovery: a verified email, a second passkey or support-led checks.
- Let users see, rename and remove their passkeys in account settings.
- For mobile apps, link the app to your domain (Associated Domains on iOS, Digital Asset Links on Android) so one passkey works on web and app.
Should you drop passwords entirely?
For most consumer apps, not yet. Start with passkeys as an option, watch how many people use them, then make them the default for new accounts. For internal tools and admin panels, where you control the devices, going passkey-first today is a sensible step that removes a whole class of attacks.
Sources
Need help with this?
Our Custom Software Development team can help you put this into practice, from the first plan to launch.
Explore Custom Software Development